Two breaches
| RockYou, 2009. 32 million passwords in plain text. Most common: | 123456 |
| Adobe, 2013. About 150 million passwords, badly encrypted, with the password hints stored right next to them | a crossword |
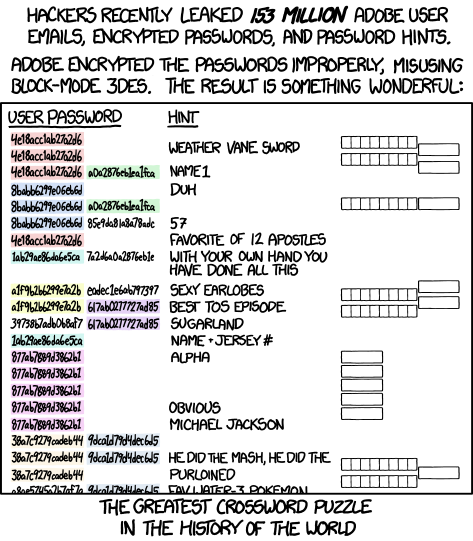
xkcd.com/1286 · CC BY-NC 2.5
Today you get to be the bad guy.
Everything you build will be used in ways you didn't intend, by people who don't wish you well. That's not paranoia. It's a design discipline.
Attackers found an employee on LinkedIn, called the IT help desk pretending to be them, and asked for a login reset. Slot machines, room keys, and check-in went down across Las Vegas. MGM put the hit at about $100 million.
Nobody broke any encryption.
Adam Shostack. MGM's help desk was part of the system. Nobody asked question 2 about it.
Talk with your pod for 20 seconds, then hands up. No reveals until all four.
аррӏе.com
Every letter there is Cyrillic. A researcher registered it, and Chrome and Firefox displayed it as apple.com, pixel for pixel. Chrome fixed it in version 59.
Its real name is xn--80ak6aa92e.com. You can't always trust your eyes. A password manager won't autofill on a site it doesn't recognize.
He pretended to be internal IT, got an employee's login, and reached an admin tool. Then Obama, Biden, Musk, and Gates all tweeted: send bitcoin, get double back. Three years in prison.
haveibeenpwned.com
Type your email. It lists every known breach your address was in.
| RockYou, 2009. 32 million passwords in plain text. Most common: | 123456 |
| Adobe, 2013. About 150 million passwords, badly encrypted, with the password hints stored right next to them | a crossword |
xkcd.com/1286 · CC BY-NC 2.5
The site never learns which one you were checking.
curl -s https://api.pwnedpasswords.com/range/5BAA6 | grep 1E4C9B93F3F0682250B6CF8331B7EE68FD8
52,372,427
A real attack on a real website, running on my laptop. It's a practice site built to be broken.
Trying this on a site you don't own is a federal crime under the Computer Fraud and Abuse Act. "I was just curious" is not a defence.
admin'#
SELECT ... FROM credential
WHERE name='$input_uname' and Password='$hashed_pwd'
It builds a sentence by pasting in what you typed.
WHERE name='admin'#' and Password='...'
I typed instructions into a box meant for data. That's the whole attack, and it has been the most famous bug on the web since 1998.
It's called SQL injection.
', salary='9999999
Every box that ends up in a SQL sentence is a door.
WHERE name = ? and Password = ?
The sentence goes to the database first, with blanks. The data goes separately. Nothing you type can become an instruction.
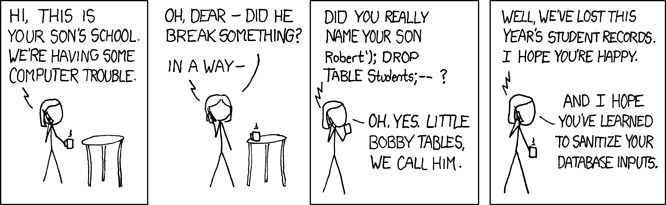
xkcd.com/327 · CC BY-NC 2.5
"Write a Python function that checks a username and password against a SQLite database."
Then read it. Find the line where the username goes into the SQL. Is it pasted into the string, or passed separately with a ?
Done early? Ask it: "Is this code vulnerable to SQL injection?" Does it fix the right line?
Your job is the part it can't do for you:
read it.
Security is the job of thinking about
how everyone else's job gets abused.
| How Computers Actually Work. Memory, processes, and what's inside the box | Wed, Oct 21 |
| Peer Mentor Meeting and its reflection. Book it today | Wed, Oct 21 |
| CS Engagement, 2 of 3 | Wed, Oct 21 |
| Ship-It. Your mentor will ask where it is. "Stuck" is a fine answer | this week |
So think like the person going around it.